Digital Forensics: From Evidence to Courtroom
From evidence to courtroom. The digital evidence course built for the justice system.
No technical background required.
Download the course overview (PDF)Digital evidence is in nearly every case. Are you ready for it?
Phones, cameras, smart speakers, and GPS data now sit at the center of investigations and trials. Digital Forensics: From Evidence to Courtroom gives the people who encounter, handle, adjudicate, or prosecute these cases the practical literacy to work with digital evidence confidently, using plain language, real-world case studies, and hands-on labs. It is the foundational cornerstone of NDG's digital forensics curriculum.
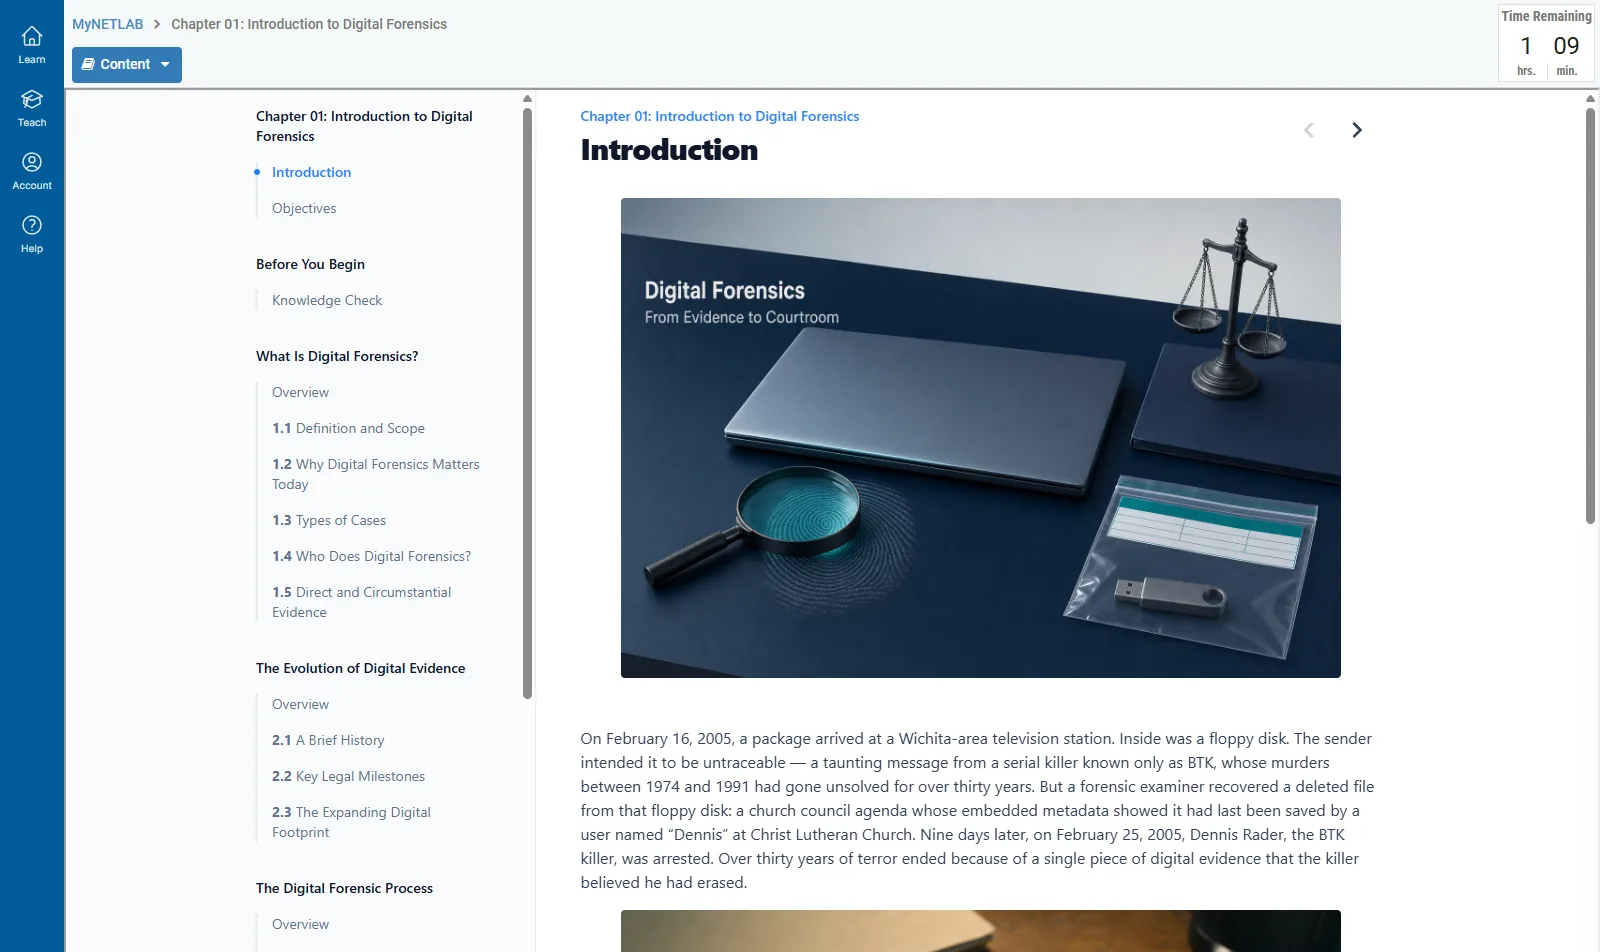
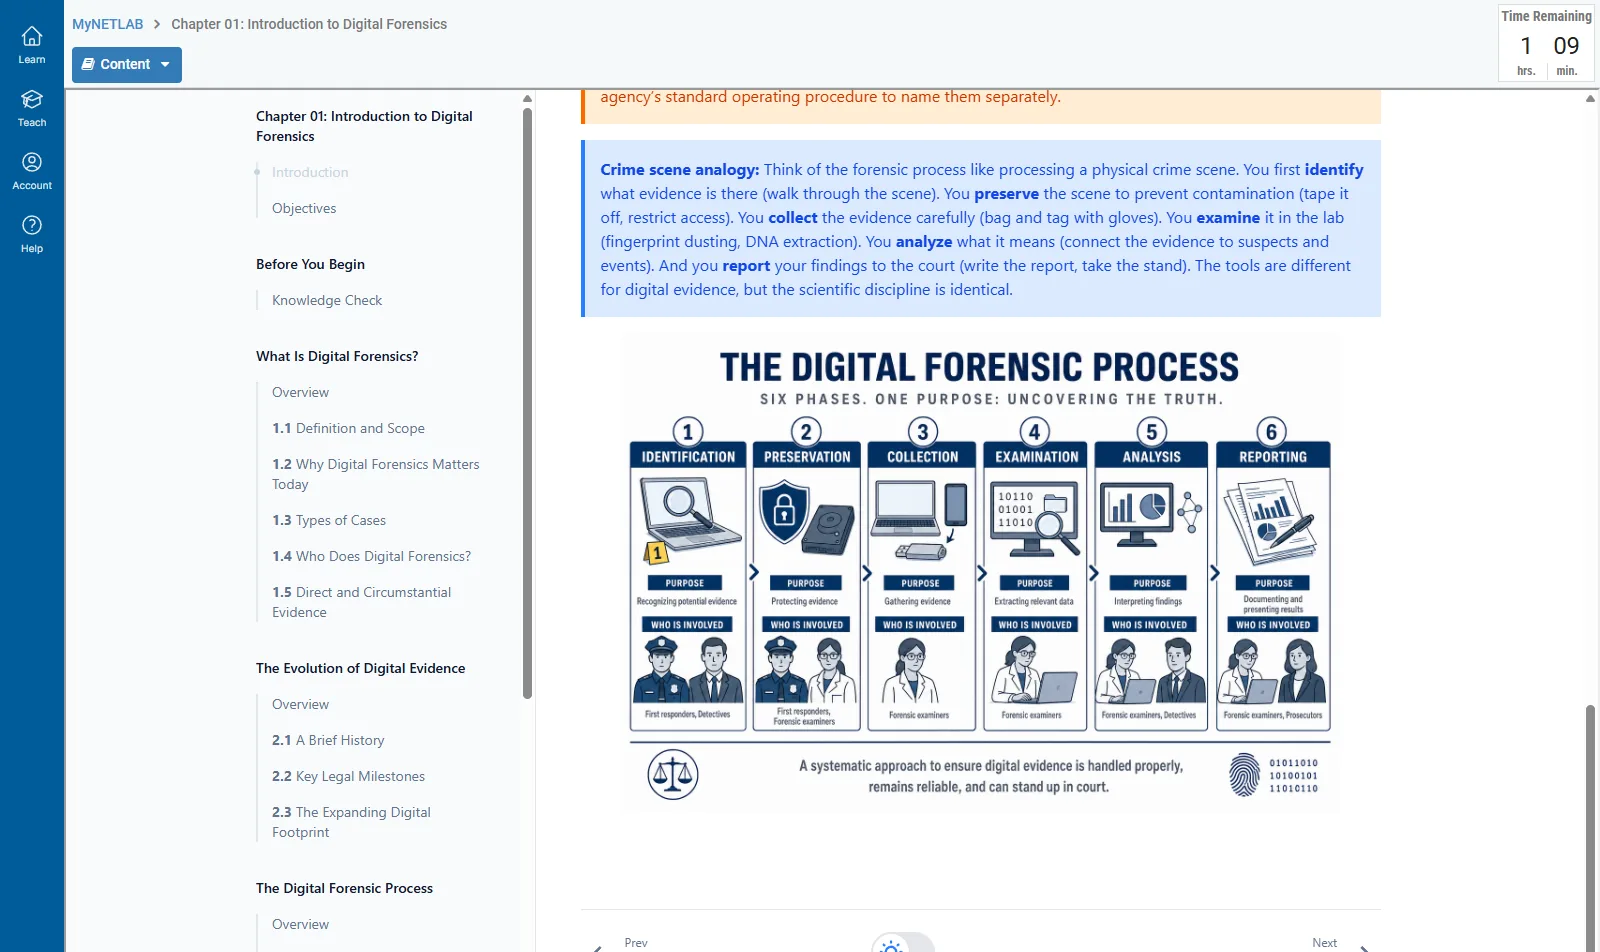
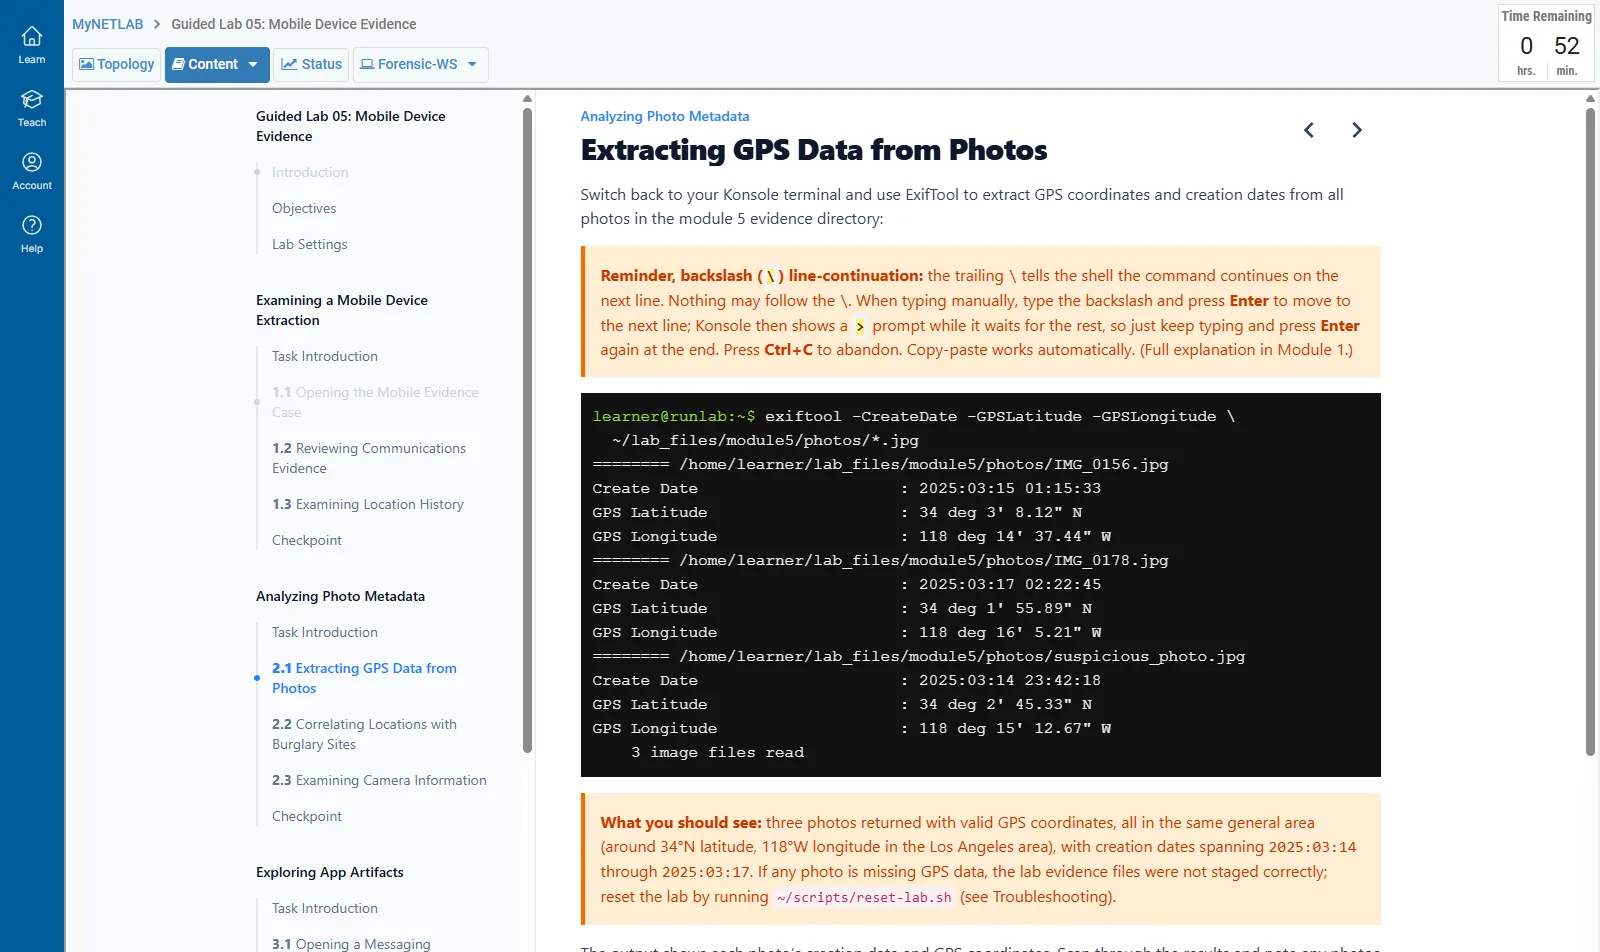
Built for the people who work with digital evidence
Law enforcement
Patrol officers, first responders, detectives, and investigators who encounter devices at the scene.
Prosecutors and attorneys
Cyber crime prosecutors, assistant DAs, federal prosecutors, and defense attorneys handling digital evidence.
Judges and magistrates
Judicial officers who rule on warrants, admissibility, and the weight of digital evidence.
Forensic paralegals
Paralegals and litigation staff who prepare, organize, and manage digital evidence.
Legal tech and eDiscovery
Legal technology consultants and eDiscovery attorneys who need fluency in digital evidence.
Investigators and new practitioners
Insurance and fraud investigators, plus learners entering digital forensics.
No prior technical or forensics experience required, just basic computer literacy.
The evidence you'll work with
Modern investigations turn on the devices people carry, drive, and live with. In this course you examine the evidence domains that show up in real cases, in a safe browser-based virtual lab.
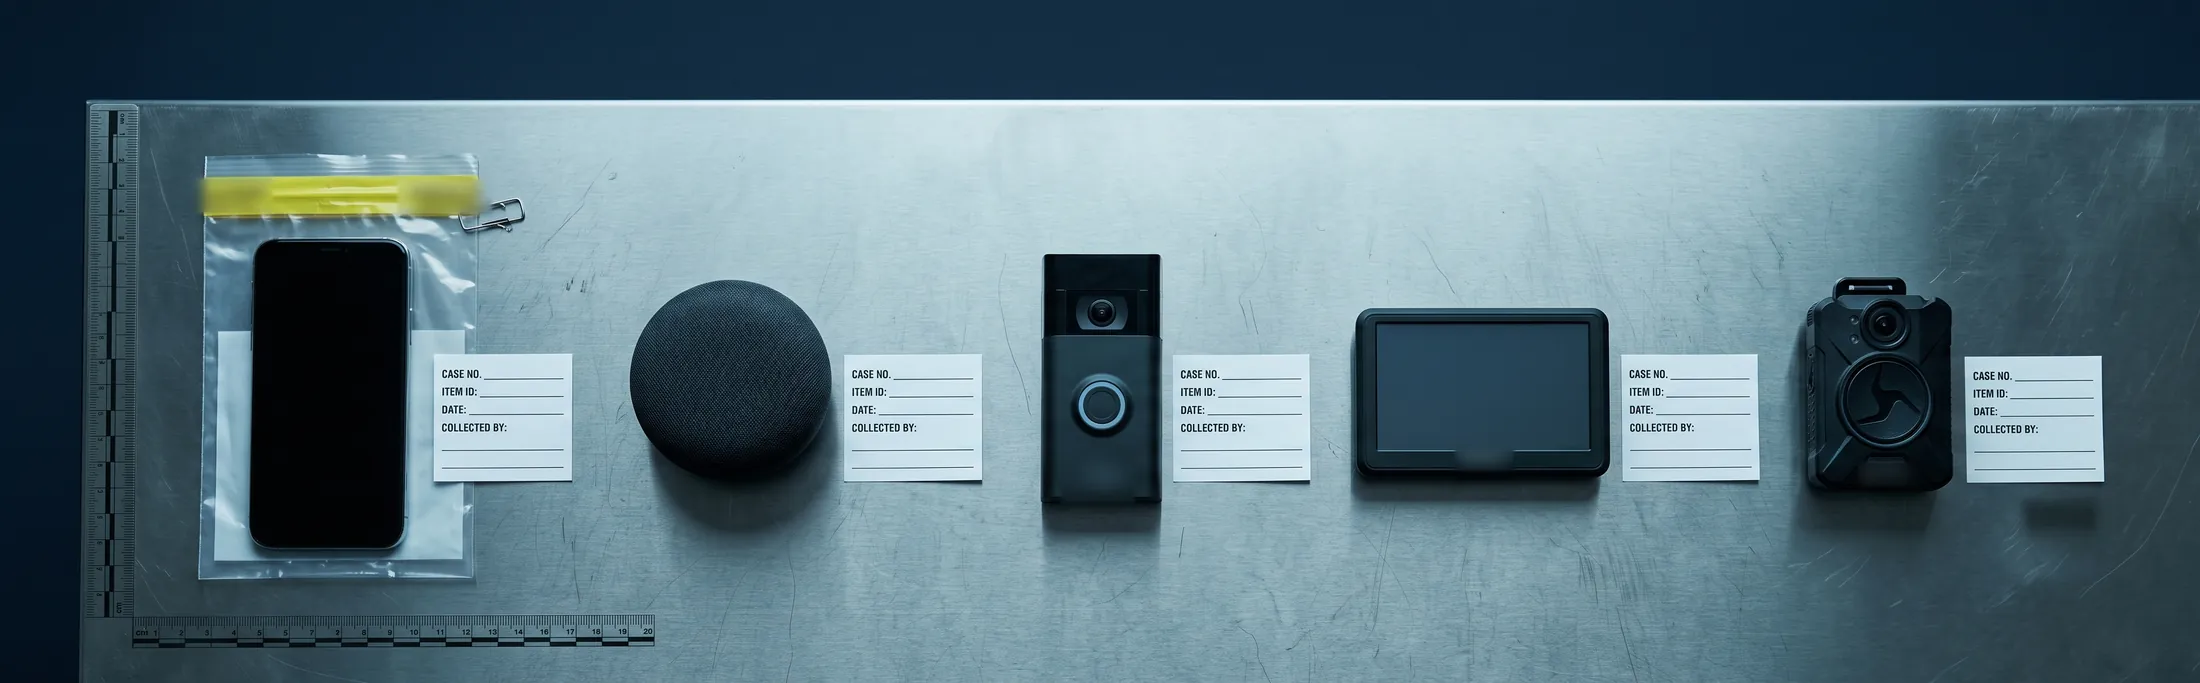
Mobile devices
Call logs, messages, photos, app data, and location history from smartphones and tablets.
Video evidence
CCTV, body cameras, dashcams, and doorbell footage: metadata, timestamps, and authentication.
IoT and smart devices
Smart speakers, video doorbells, and home automation logs, and where that data actually lives.
Vehicle and location
License plate readers, GPS tracking, and cell-site location data, including the law that governs them.
A dedicated module covers AI and emerging technology: AI-assisted analysis, deepfake detection, and the reliability of AI-generated evidence.
From the crime scene to the courtroom
The course follows digital evidence through its entire life cycle, so you understand not just what the evidence is, but how it holds up when it matters most.
- Identify digital evidence across mobile, video, IoT, and location domains
- Apply the legal frameworks that govern collection (Fourth Amendment, ECPA, SCA, and Carpenter)
- Follow first-responder protocols so evidence isn't lost or excluded
- Draft warrant language for phones, cloud accounts, IoT devices, and location data
- Recognize how evidence is authenticated and challenged under Daubert and Frye
- Examine evidence with foundational forensic tools in a guided environment
Tools you'll use
You work in a real forensic workstation that runs in your browser. Nothing to install.
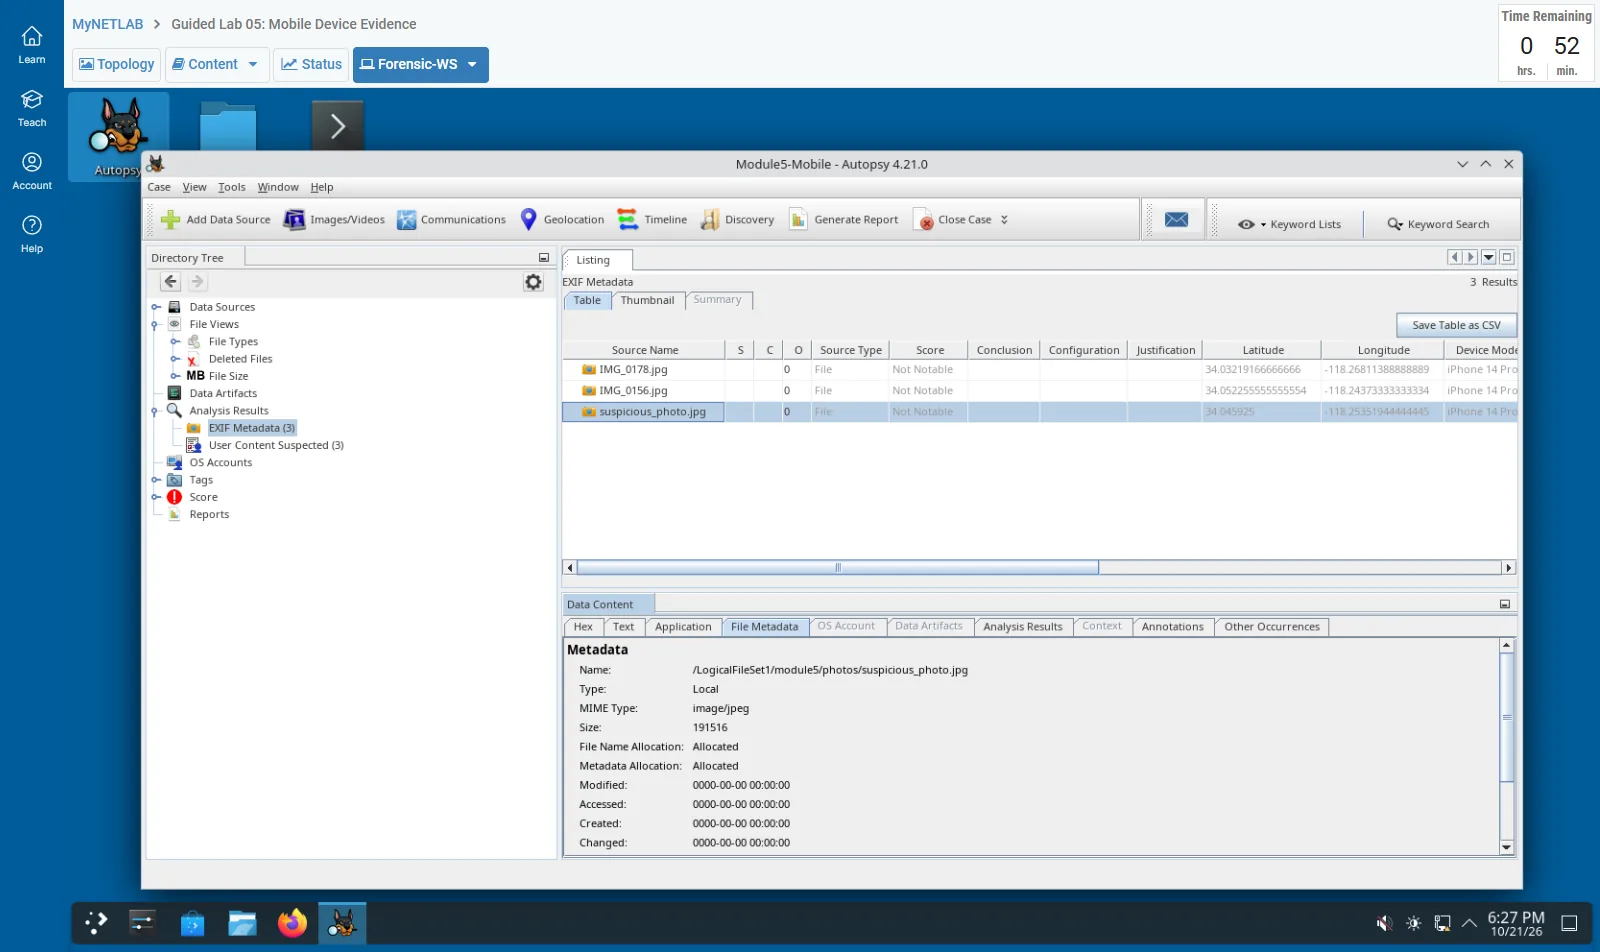
- Autopsy: disk image and device analysis
- ExifTool: metadata extraction
- MediaInfo: video and audio analysis
- SQLite Browser: mobile app databases
All evidence is fictional and synthetic. Labs run fully sandboxed, with no real case data.
What's inside: 12 modules, 24 hours
Each module pairs plain-language instruction with a quiz. There are 18 labs: 9 guided, with step-by-step instructions and hints, and 9 applied, which give the same scenarios as tasks and grade at the end. The course finishes with an end-to-end case simulation.
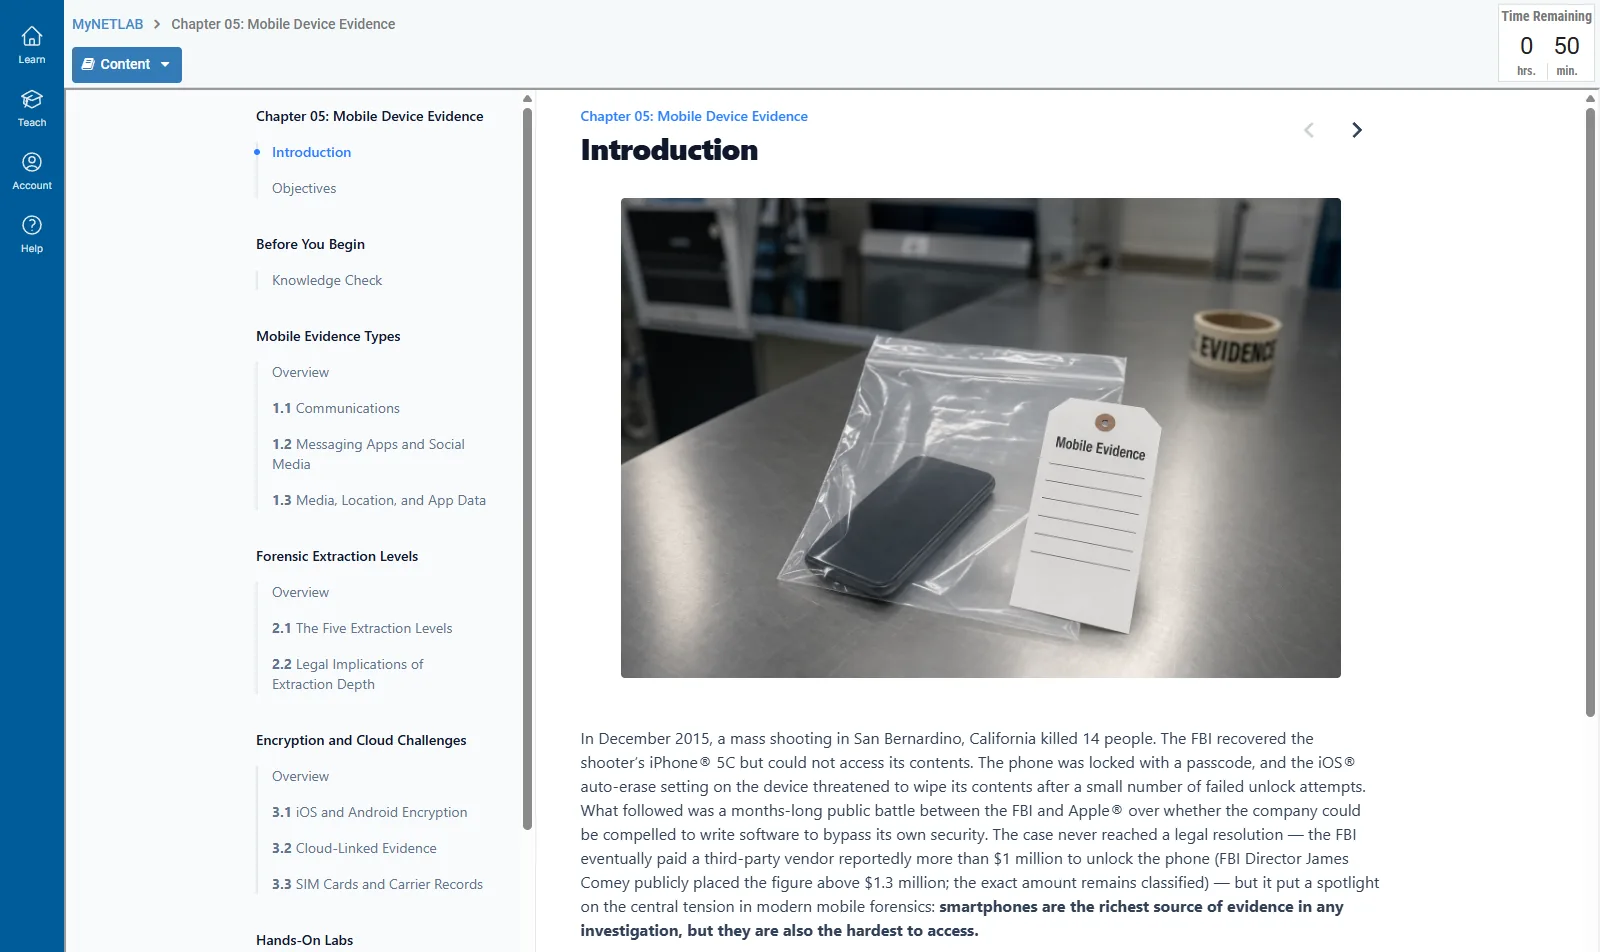
Next in the curriculum: Digital Evidence: Collection, Acquisition & Preservation, which takes seizure, imaging, and chain of custody to working proficiency. See all digital forensics courses.
How the course maps to certifications and frameworks
The course maps to foundational objectives from major digital forensics certifications and to CompTIA Security+. It also aligns with the NICE Framework, NIST SP 800-86, SWGDE standards, and DOJ electronic-evidence guidance.
Maps to foundational objectives. This course is not a certification exam or a guarantee of certification.
Common questions
Do I need a technical or forensics background?
No. This is a foundational course written in plain language for justice-system professionals. You need only basic computer literacy: opening files, using a web browser, and navigating a desktop.
What digital evidence does the course cover?
Mobile devices, video (CCTV, body cameras, dashcams, and doorbells), IoT and smart-home devices, and vehicle and location data (license plate readers, GPS, and cell-site location). A dedicated module covers AI and deepfake evidence.
Which certifications does DF-101 map to?
It maps to foundational objectives from IACIS CFCE, ISFCE CCE, GIAC GCFE, and EC-Council CHFI, and to CompTIA Security+. It also aligns with the NICE Framework, NIST SP 800-86, SWGDE standards, and DOJ electronic-evidence guidance.
How long does the course take, and what tools will I use?
About 24 hours across 12 modules. You work with Autopsy, ExifTool, MediaInfo, and SQLite Browser in a forensic workstation that runs in your browser, with nothing to install and no real case data.
Can I bring this course to my agency, department, or team?
Yes. You can teach it in a class or buy access for a team. Use the 'Teach this in a class' option to set up a class, or contact us about team and bulk options.
Delivered on NDG Online
NDG Online runs the lab environment right in your browser, with no installs and no hardware. Network Development Group has built lab-based IT training for educational institutions, government, and industry since 1999. The course uses NDG's "practice as you read" approach: coursebook, labs, and assessments together.
Running your own NETLAB+ system? The labs are also available as NETLAB+ supported content, delivered on the NDG Digital Forensics v1.0 pod.
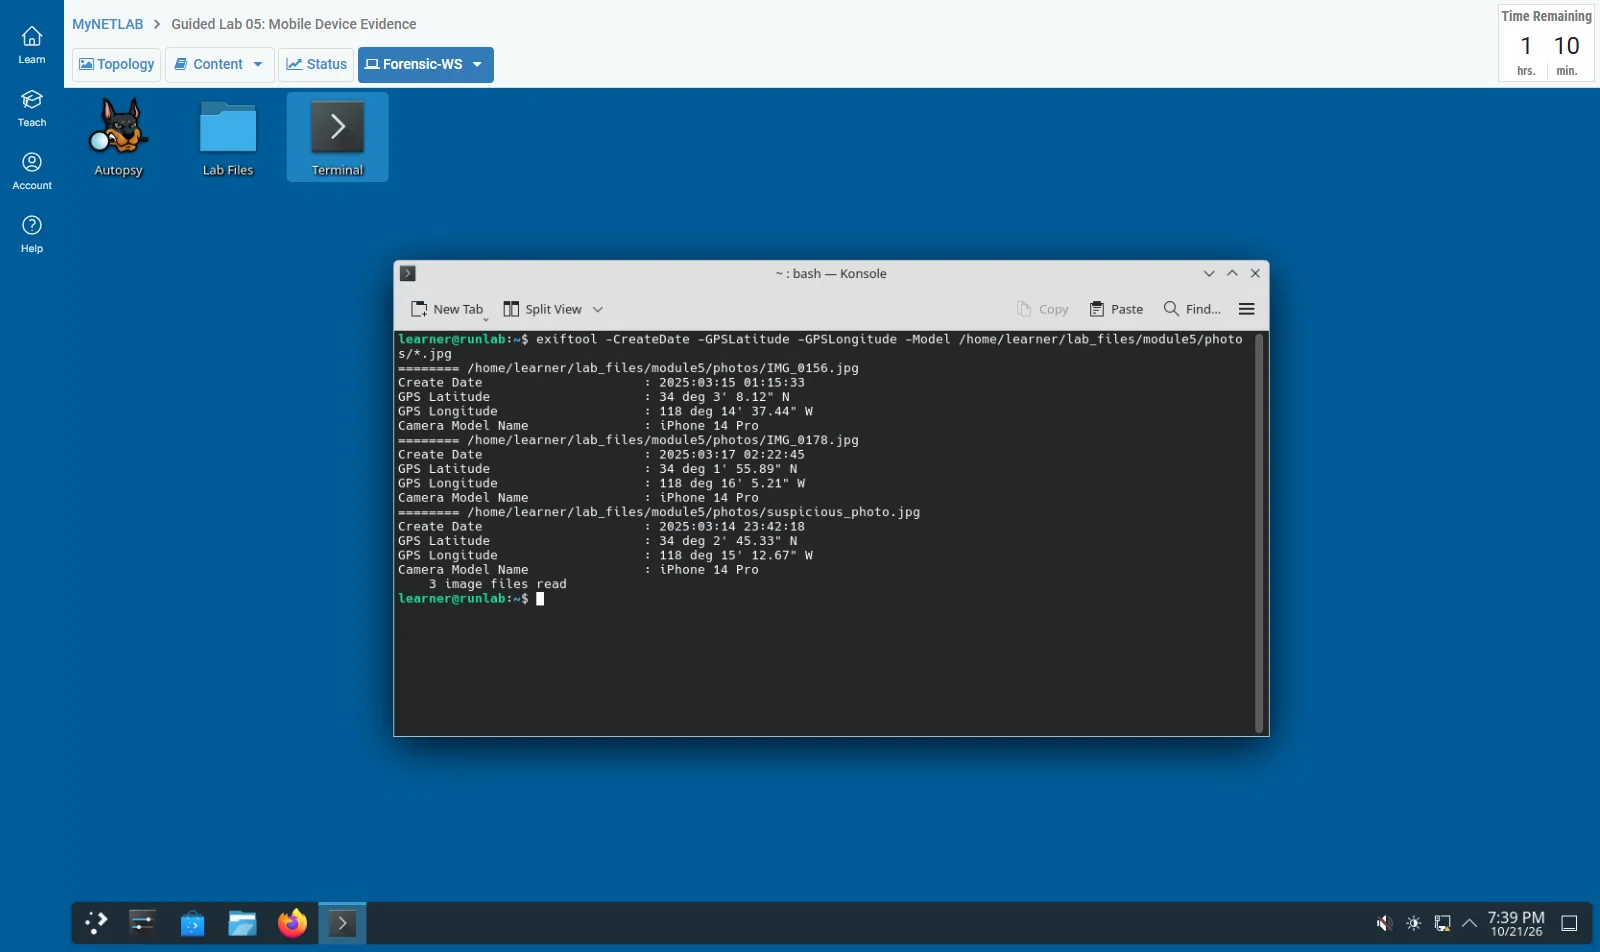
- Readable, plain-language coursebook
- Two lab versions: guided (with hints) and applied (tasks only)
- Quizzes and a final case simulation
- Practice-as-you-read approach